Approved topology implementation
Implement the scoped spine-leaf or other approved topology, coordinating device placement, port assignments and network-owner decisions with the rack build and intended endpoint connections.
Connect the topology to the installed reality
Compute and storage depend on a fabric that matches the design at every connection. O-Connect brings physical links, network implementation and verification into one delivery workstream, helping the project account for the data, management and out-of-band paths that technical teams need to commission and support the environment with confidence.
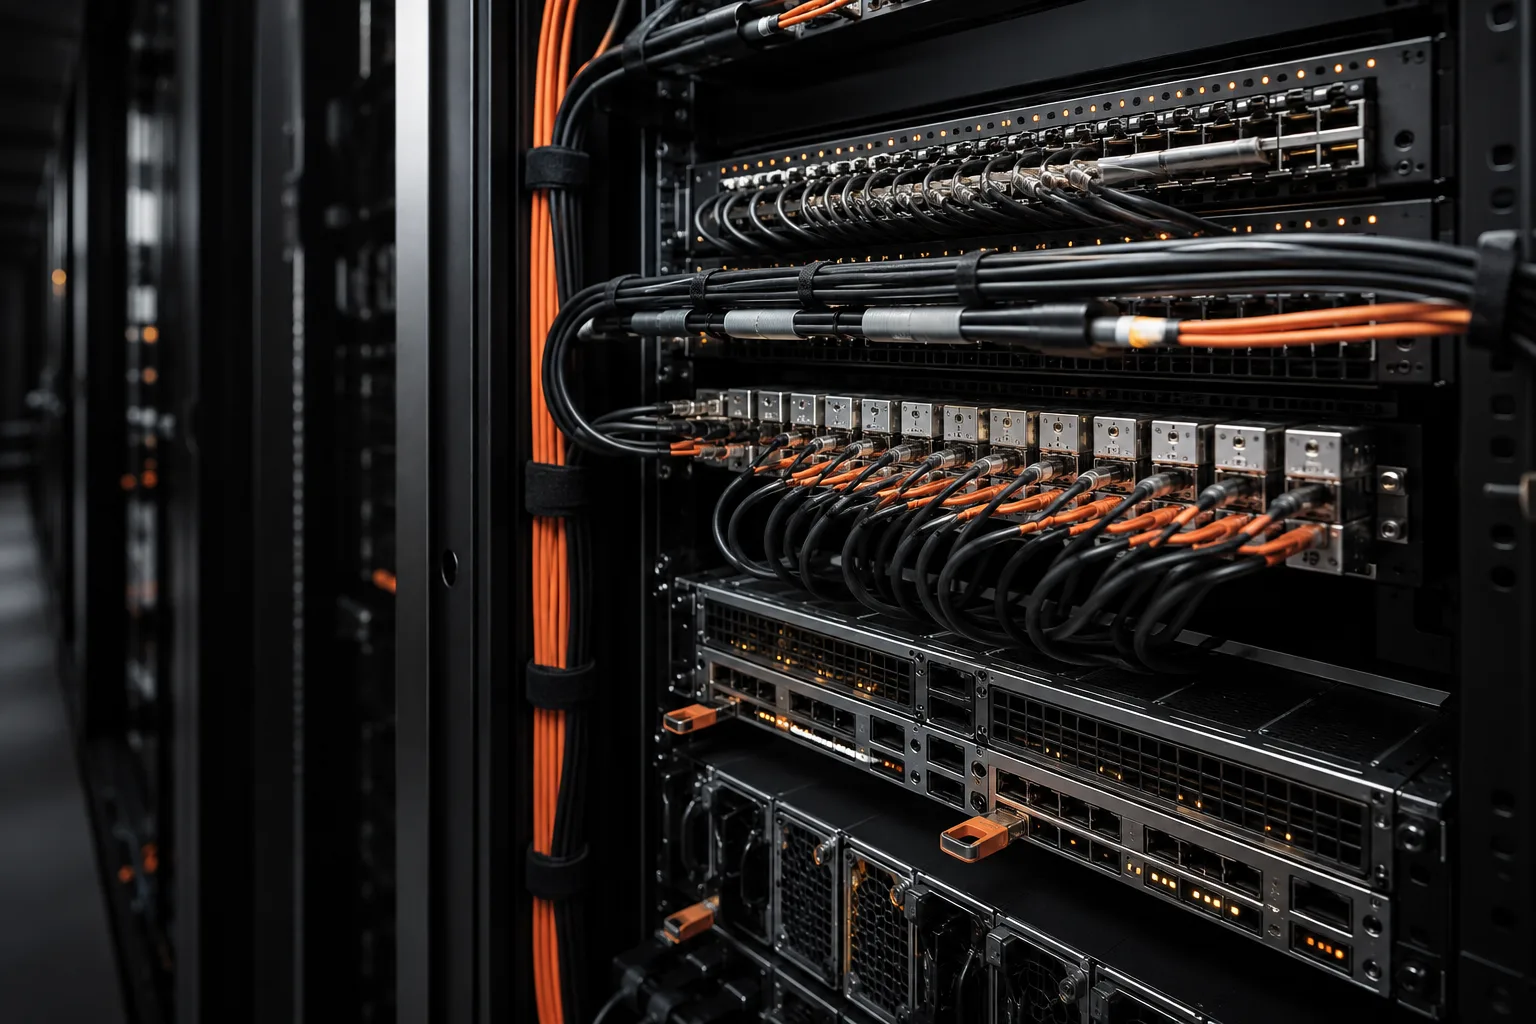
The approved topology provides the starting point: device roles, port assignments, logical networks and the intended connections between compute and storage. O-Connect aligns this information with the installed equipment and cable records, then coordinates the implementation scope with network, platform and storage owners so interface decisions are settled before they become commissioning issues.
Verification follows the intended path through the system. Link state and port identity are useful evidence, but the acceptance plan also needs to account for logical connectivity and the endpoints the environment depends on. Results, configuration records and exceptions are brought together so the network handover describes what was implemented and what was actually checked.
Implement the scoped spine-leaf or other approved topology, coordinating device placement, port assignments and network-owner decisions with the rack build and intended endpoint connections.
Bring up the agreed fabric within the approved architecture and configuration scope, recording its baseline and the dependencies needed from compute, storage or vendor teams.
Coordinate the management and out-of-band networks defined by the design, keeping their intended connections and ownership clear in the implementation records and acceptance plan.
Check agreed paths against the topology and acceptance criteria, recording relevant link, port and logical-network evidence alongside findings that require correction or owner review.
Review topology, port maps, cable records and endpoint dependencies, then establish the configuration baseline, change authority and verification scope with the appointed network and platform owners.
Coordinate physical and logical implementation in the agreed order, capturing changes and exceptions so the working configuration remains traceable to the approved design and scope.
Complete the agreed connectivity checks, review findings with technical owners and assemble the topology, port records, configuration position and test evidence for operational handover.

The network handover connects topology, port identity, configuration records and verification evidence in one usable view. Compute, storage and operations teams can see the intended paths, the tested position and any unresolved dependencies, supporting a more informed acceptance decision and clearer ownership after the deployment.
Define your acceptance criteriaThe scope can cover either fabric where it is part of the approved architecture. The project review establishes the equipment, configuration requirements, responsible technical owners and acceptance checks for the chosen design, including its dependencies on compute and storage.
Management and out-of-band paths can be included as defined workstreams. Their topology, access requirements and ownership should be documented alongside the data network so implementation and verification account for the operational connections required by the deployed platform.
Acceptance demonstrates the results of agreed checks under documented conditions. Application performance also depends on the workload and connected platform. Any workload-specific tests, target conditions and owner responsibilities need to be defined in the acceptance plan before results can be assessed against them.
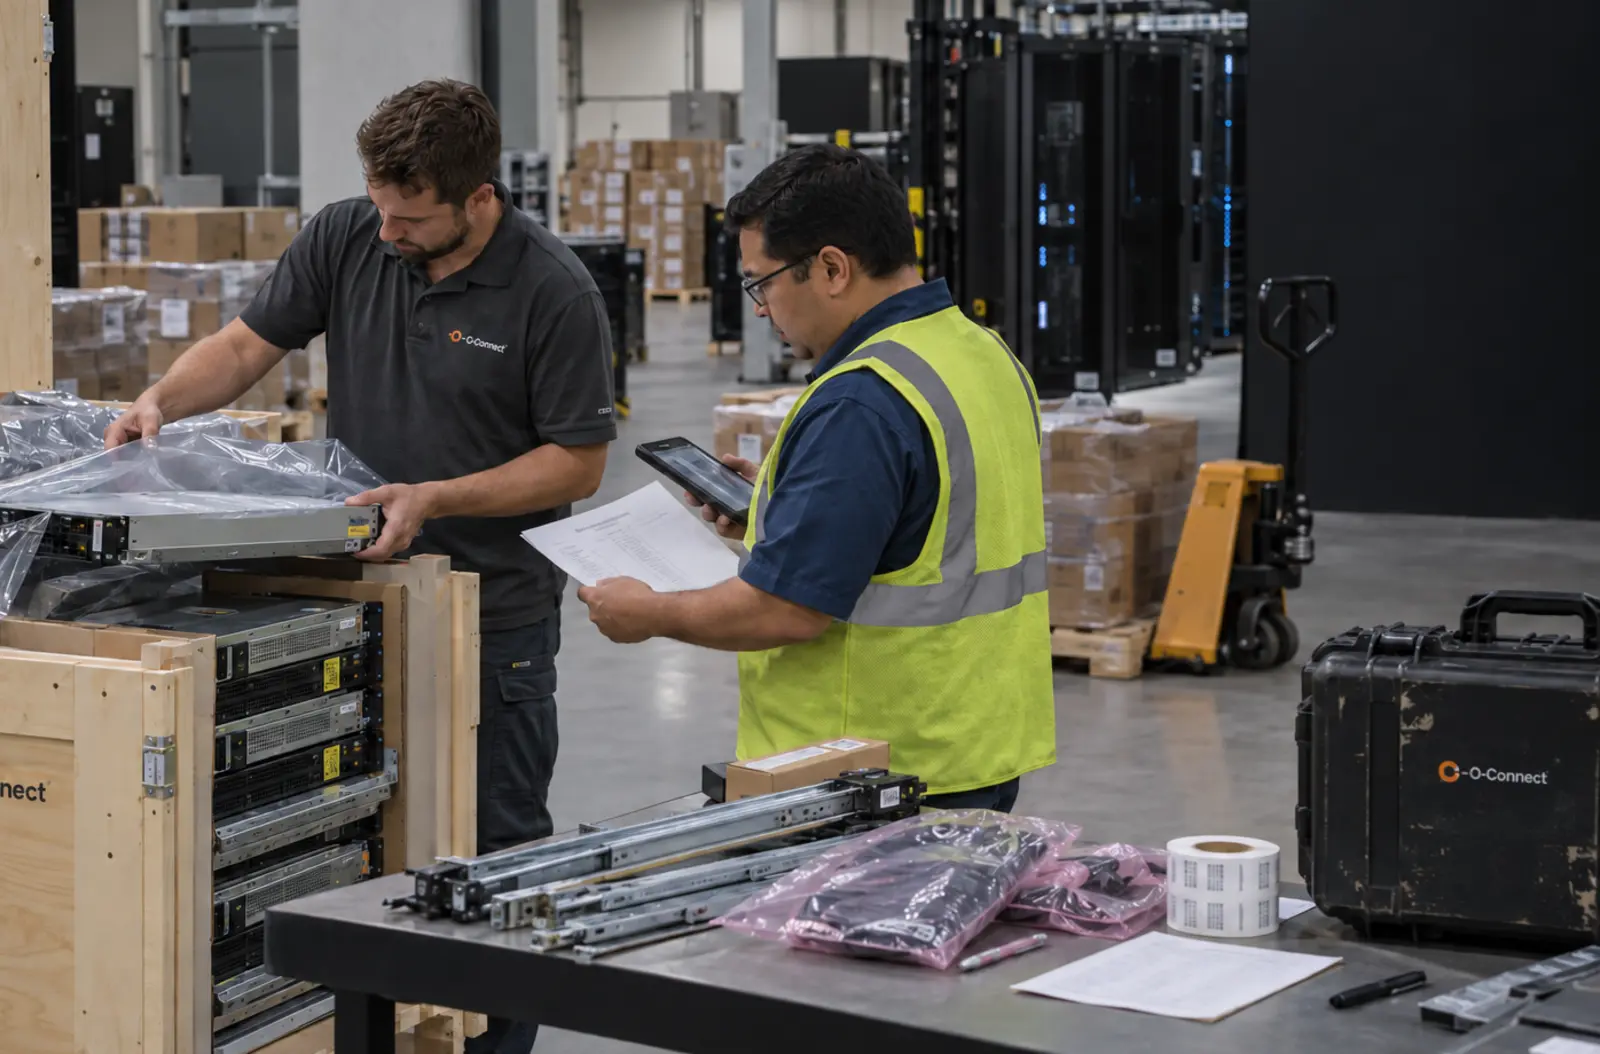
Turn delivered equipment into an installed, labelled environment with asset reconciliation, approved rack builds, cable installation and as-built records.

Coordinate GPU nodes, fabric, storage and platform baselines through AI cluster deployment, with defined dependencies, health checks and acceptance evidence.
Coordinate infrastructure deployment with controlled access, segregated network paths and traceable records aligned to your approved site requirements.